eclipse kepler (4.3) on a mac

Getting started

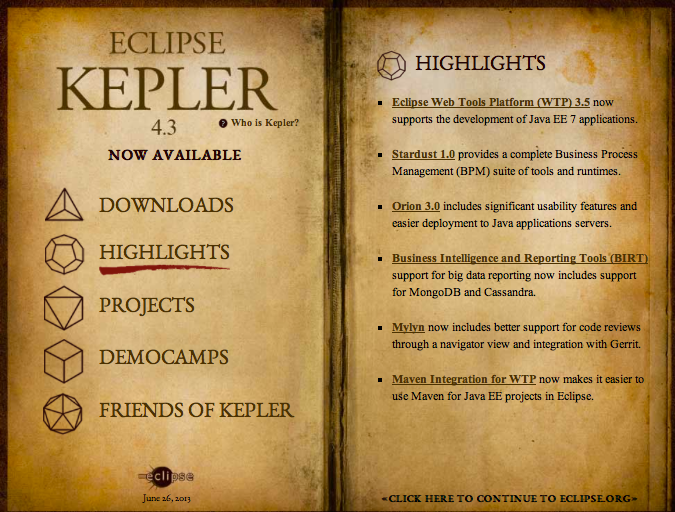
When going to the Eclipse site, I was greeted with a cool book looking page about Kepler.  Who Kepler is, what’s new, the link to download, etc.  kepler-book
Choosing a package

Eclipse has a nice chart comparing the features in each edition.  I’m excited to see git and maven got promoted to the Java EE edition.  In fact the Java EE edition is *almost* a superset of the Java edition now.  The download is 50MB bigger than last time.  And since Verizon wired the basement for FIOS but not any individual apartments yet, this means 30-45 minute download.  Now that I have the file eclipse-jee-kepler-R-macosx-cocoa-x86_64.tar, I can start.

Installing on A Mac was a small adventure

I did the usual of untarring and copying the eclipse folder into Applications.  I got an error: “Eclipse” is damaged and can’t be opened.  You should move it to the Trash.

I found a command here to get Gatekeeper to allow it:  xattr -d com.apple.quarantine /Applications/eclipse/Eclipse.app

Then I got: Failed to load the JNI shared library /Library/java/JavaVirtualMachines/1.7.0.jdk/Contents/Home/bin/../jre/lib/client/libjvm.dylib

I was on Java 7 update 17.  I updated to update 25, but that didn’t help.  I then tried using a launch startup script per the bug report.  Note that I needed to change two bolded lines to point to my install location.

#!/bin/bash
/Library/Java/JavaVirtualMachines/1.7.0.jdk/Contents/Home/jre/bin/java \
-Djava.library.path=<strong>/Applications/eclipse/plugins/org.eclipse.equinox.launcher.cocoa.macosx.x86_64_1.1.200.v20130521-0416/eclipse_1507.so</strong> \
-Xms512m \
-Xmx2048m \
-Xdock:icon=../Resources/Eclipse.icns \
-XstartOnFirstThread \
-Dorg.eclipse.swt.internal.carbon.smallFonts \
-XX:MaxPermSize=256m \
-jar /Applications/eclipse/plugins/org.eclipse.equinox.launcher_1.3.0.v20130327-1440.jar \
-os macosx \
-ws cocoa \
-arch x86_64 \
-showsplash \
-name Eclipse \
--launcher.appendVmargs \
-debug

It sounds like this will be fixed in Kepler SR  1.  In the meantime I renamed my script to end in .command so I can open it via the applications finder window (nice tip)

First Impressions

Since some of the plugins I was using are now built in and others I don’t use anymore (that I installed over the past year), I decided not to import my plugins from a previous installation and start anew.  It’s easy enough to install from the marketplace.

The significant plugins I use:

Plugin Purpose
Mongrel Tomcat integration supporting Tomcat 7.  (The version of Sysdeo I was using seems to have had that too but at least Mongrel looks more active.) Used the Sysdeo source code and forked it since Sysdeo isn’t getting updates anymore.
Ecl Emma Code coverage
PMD and FindBugs Static analysis
Subversive To access Subversion repositories
Groovy/Grails Tool Suite Groovy project/editor and console
Eclipse Memory Analyzer For finding memory leaks – must use update site rather than marketplace
Freemarker IDE Freemarker syntax highlighting and macro assistance.  Note that it is listed under the JBoss Tool Project.
Papyrus UML editor – under install new software > kepler > papyrus  (I don’t recommend Papyrus at this time.)
Python Python plugin/perspective

What excites me

  1. Mylyn connector improvements (for code review)
  2. Remove type arguments after content assist – this happened just often enjoy to be annoying
  3. IDE support for JUnit Assumptions

What frustrates me

  1. The mess about Mac support for Kepler.  It’s annoying launching from the command line (or even a command).

blogging from owasp security meetup

The NYC Cyber Security meetup had Jeff Williams as a speaker.  He’s really good so I decided to go and blog about it.  All three sessions were really good!  Which sets good expectations for the Appsec USA conference which I’m thinking about attending in November.

Before we move on to security – a bit of humor.  I asked where the ladies room was and an employee pointed at what appeared to be the elevator bank.  On the end was a door with the word “womens” on it.  It looked just like the wall.  Camouflage!
Jeff Williams from Aspect – Is OWASP the New Rainbow Series?
Jeff is a very dynamic speaker so this was fun.
Rainbow series and security models
  • The Rainbow Series is colored pamphlets/thin docs.   Stopped printing due to internet.  Community evaporated and group folded. Info still holds – access control, encryption, etc. nobody shepherded knowledge over tech gap.
  • Security IMPLIES a model –  what does security mean?  Possibilities include: policy, no high exploitable vulnerabilities, standards, compliance , your tool’s ruleset, what pen tester interested in, whatever just got hacked (reactive). Need a model to say secure. Compliance is what others care about.  It’s like delegating your security model to someone else.
  • Rainbow had positive view – assurance world.  said controls must be analyzable – must know if good. Completeness, patterns, policy, etc.
  • OWASP uses a negative model. Top 10 is what thou shalt not do. Negative model is harder, but ok.   Current world is negative and risk based. Assume ok until prrove otherwise.
  • Goal – rational, defensible, confidence that our apps are “secure” – id important threats, strong defense for each, implement correctly and evidence defenses are working
Coverage
  • Code coverage – Static analysis tools only look at your custom code. They don’t look at libraries, frameworks, app server and runtime.  Only a small percent covered.  On the dynamic side we hit all te layers but only part of the app. 25-30% is typical.
  • Weakness coverage – NSA has a test suite called Juliet. You run static analysis against it to see how good the tool is. Found 80% failing test and more than 60% false alarms.   And Juliet is less complex than code real apps would have.
  • Portfolio coverage- most apps unreviewed because not critical. A small percent are scanned/penetration test.  And an even smaller portion get manual code review
Aspect Top 10 
  • Jeff hates top ten lists  Negative, incomplete (for example: clickjacking not in top 10), abstract (all of session management in one item), arbitrary, retrospective. Not a good model.   [This is sort of in jest as he does find them better not thing; it’s more frustration that we haven’t moved on]
  • Was needed in 2002.  Goal was to set a bar so can keep raising bar.   That didn’t happen. First top 10 was forward looking. Then started relying more on data and people doing reviews.  This is a problem. Because auditors behind casual hackers and way behind organized chrime and espionage. Compare to the crypto community who looks at what the threat will be in 10 years.  Better capability,better tools.
  • Owasp top 10 is most widely used project at owasp.  Failure because nothing has changed.  Also biggest success because raised awareness.
  • Security efforts and tools focused on apps of 2005. Not ajax, sockets, gwt, html 5, inversion of control, aop
A9 in top 10 – using components with known vulnerabilities  
  • New to the top 10.  (In case you are wondering, nothing got removed.  Insecure cryptography and insecure transport layer got merged.)
  • Reddit quote:  “One of the vulnerabilities is having known vulnerabilities”
  • The amount of custom code in our apps hasn’t changed much in 10 years. Amount of library code growing quickly. Now 80% library code. Hudson core has 103 open source library.  You are trusting ALL that code on your machine.   Dependency resolution brings in other dependencies so don’t know what using.
  • One single vulnerability (cve-2010-1622) on spring beans tainted 1447 projects!
  • Developers don’t update libraries in general. Sometimes not using that part of project. Some bad like spring EL injection policies
  • 2313 organizations using esapi and it is built into cold fusion
  • Rougly 26% libraries are vulnerable.
  • Maven can list what libraries using
 What to do
  • Focus on soeed and scale. If need an expert for technique or tool, introduces feedback lag and cant scale. Looks good for one app.  Which causes pressur to compromise on scope and accuracy to increase throughout.   Better to use experts to id threats, build automated tests, create rules, strategy, etc.   security HAS to work in parallel.
  • See if can embed sensors in app and report back data about security. Instrument code and organization so it feeds you info. Think big data.
  Panel – from Morgan Stanley – the hosts (I confirmed with the moderator from Morgan Stanley that it is ok to blog)
Securing the enterprise – what means to you
  • Protect developers from selves. Not have to think too much about what take off shelf and put in app
  • The enterprise used to be a building when gates, guards and guns were data security because thats where the data was.
  • Now have to worry about employees sending stuff out ,  not just attackers coming in.   Threat landscape changes, tech advances quickly. If rush and hurry, can roll out globally in 12-18 months
 What would you do if owasp releases new findings?
  • New data – threat intelligence – can mitigate, detect or respond with technologies in house. Big enough to have a team of people will full time jobs focused on this.
  • Financial industry grouos to share info. Move in a pack. Exchange info.
  • In small company with 20-30 apps can have one guy look at it. hTis doesnt scale to 20,000. Need to know what apps and people permitted on network
Thoughts on mailing plaintext passwords
  • Finanical sector means saving for 7 years in an archive.  Authentication and sso – have internal docs for developers so get this right so doesn’t happen.
  • Importance of keeping your personal email account secure.
  • Different passwords for all sites, password management system. Beyond what the average person will do. Need to hold system accountable. Shouldnt be able to email password to user.  [I’m surprised nobody mentioned two factor for email – I use that for gmail.
  • Need to give vendors feedback so can improve
  • Discussion on standard self declaration of password handling practice.   Another panelist refuted because additional intelligence – “if they know that, they wouldn’t be emailing you your password”. Don’t want it to be a hitlist when a vulnerability comes out.
  • Jeff Williams from audience said likes idea of making model public.  Morgan Stanley folks cringed. View as challenge or a boast. Jeff said make public internally.   Financial sector – you know what minimum standards are. For internet sites, don’t know threshold. Only held to FTC 15 years of supervision after breech.
Is data the thing that enables us to move into the future?
  • Data has always been at the core. After a breech, one of the first questions is what did they get.
  • Libraries should have an end of life or expiration date so doesn’t last with vulnerabilities forever.
  • Ability to process the data is catching up.  Easier to find the holes. And what went thru that hole
  • From vendors – need better metrics and inteligence. Currently get more graphics not intelligence
  • Can get badge saying ran automated scanning tool against site
Standards
  • New perimeter – bring your own device (BYOD) – access corporate intranet from whatever device
  • No such thing as a perimeter any more.   Or more perimeters on the inside. Not dead. Can’t just trust the inside. Contain breech. Compartmentalize.
  • Bring your own tech – bringing network connections too – Starbucks is in your enterprise
  • What enterprise thinks it can control will shrink – byod, cloud, paas, saas
  • If 20 person company, have a lot more control
  • On the AP Twitter hack (white house bomb false story.)  It affected the market because some high frequency trading was keyed into twitter.  This is the danger of being first and fastest.  Corners cut.  Want to know about twitter but not automated based on it.  Is Twitter in your security perimeter?
  • Cant just have tech. Need policies to back up. So can enforce and prosecute. Need management support
  • Wouldn’t consider having just 1 isp. If all 5 isps under siege, trading is the least of your problems. Extreme resiliency
  • Wouldn’t care if password policy published. Not a surprise because know vague idea in finance. Thousands of people. Every year. Assume info is out there. And give info to suppliers for confidence
 Tom Brennan -Trustware global security report
The report contains a collection of interesting stats.  You can read the report online (or at least last year’s version; see the resources section below for the link).
  • They focus on monetary loss.
  • Top victims – us, australia, canada, uk, brazil
  • Top attackers – romania, us, unknown, ukraine, china
  • Websites and email most utilized vector
  • Mobile malware on the rise
  • Breach quadrilateral – propagation, aggregation, exfiltraton, (how get data out of environment) and infiltration. – much emphasis on perimeter but not propagation. Once gets in, need to be able to stop. If can stop any phases, you beat the bad guy
  • 82% of apps they looked at have xss and 72% csrf. Wow. I shouldn’t be surprised.  CodeRanch only fixed CSRF (read about how) this year.
  • What  to do: Train developers, Review code, Test a lot, Protect in real time and patch

Mobile

  • Mobile malware up 400% last year. Top findings are insufficient cache controls, replay attacks on sensitive transactions, sensitive info in server response.
  • Use case: Malicious game sends hidden sms messages. Similarly can use receiving hidden sms to launch botnet
  • Apple did better job than android.  Android kitered with malware
  • Can’t patch. With byod, phone not owned by company
Spam
  • Spam down to 2007 levels but nearly 7% of spam links to a malicious website.
  • Still 75% ompanies email is spam

Passwords

  • Weakest links are employees and users
  • Password1 is 38% of top 25 password
  • Lot of passwords are top child and dog names for reset questions
  • Peak password length is 8 characters because default active directory minimum length
Six security pursuits
  • visualize events
  • unify activity logs
  • register assets
  • educate employees
  • identify users
  • protect data
Problem: Businesses focus on making money in version 1 and security in version 2. And then forget about version 2
Resources
I learned about the following at the event:

intro to web accessibility

Someone asked me what someone should know/read as a crash course on web accessibility.  This seemed like too good a question not to blog about so he can read the answer here!

There are three main areas of web accessibility:

  1. W3C’s WAI (web accessibility initiative) has WCAG 2 (Web content accessibility guidelines) which are summarized on one page.  There’s a lot more to it than the one page, but it does represent the spirit.
  2. WAI also has ARIA (accessibility rich internet applications).  This is my favorite description.  Mozilla also has a good guide as does Opera.  In a nutshell, ARIA solves the problem of “how does a blind user know something on the page has changed.”  With AJAX and even DHTML, just because you made something available isn’t enough.  Be forewarned that older browsers have lousy ARIA support if any at all.
  3. Section 508 is in the same space as WAI except for government website.  It is part of the American with Disabilities Act.  It is more specific in some ways than WAI.  If you aren’t working on a government website, I’d focus on WAI.  Note that Section 508 is an OLD law and in theory they are working on a refresh.  I say in theory because I haven’t seen updates in a while.  There is a mapping in section 1194.22 between Section 5098 and the WCAG 1.0 guidelines.  Yes, 1.0.  Did I mention that Section 508 is old?  The government has free training.

The least you need to know for testing:

  • Make sure your application works without using a mouse.  Seriously, actually navigate your application without a mouse.  (Remember tab changes fields and space selects a checkbox.)  If it isn’t possible to use the application without the mouse, you have failed accessibility miserably.
  • Make sure you aren’t using color alone to convey information. Blind people will be using a screenreader and need alternate textual ways to derive this info. Colorblind can’t see the difference between red and green and won’t be using a screenreader so won’t see your alternate text.
  • Until you are REALLY familiar with how text only navigation works, use a screenreader emulator like the Fangs Firefox plugin and/or turn off stylesheets to see what your page looks like.
  • If you can afford a license for Jaws, it is helpful in testing that your application is accessible in practice and not just theory.

The least you need to know for coding:

  • For any image that conveys information, have an alt attribute.
  • Use form labels for all form elements so a screenreader can read what the form element is all about.
  • Use row and or column headers for all data tables so a screenreader can provide assistive text on where the user is in the table.  (And for the love pete, don’t complicate things with the navigation tables of the 90s)
  • I recommend automation to ensure you KEEP compliant.  It’s a pain to test this all once manually.  You don’t want to have to make sure the new person on your team remembered his/her alts.
  • Watch how you use JavaScript: Remember we need to work without a mouse.  That means an onchange handler in a pull down is the path to madness.  I want the fifth element so I tab to the field, choose the second, watch the page refresh, tab to the field again, choose the third, watch the page refresh and then decide never to do business with you again.
  • Some JavaScript libraries have accessible widgets.