security war stories – shuman ghosemajumder – qcon

For my other blog posts on QCon, see the live blog table of contents. Shuman is from ShapeSecurity and used to be the “Click Fraud Czar” at Google – which protects AdWords from malicious users.

  • “Computer security is like broccoli. You know you should have it but would rather have chocolate”
  • “My objective today is not to scare you, but it doesn’t necessarily hurt”
  • “If I were legally responsible for the security of the software I wrote, I would quit my job immediately … and probably move to a non-extredition country” – anon at QCon

How make completely secure

  1. Get rid of business model
  2. Don’t connect to internet

Security is relative – really about tradeoffs

History

  • 1903 – Marconi showing telegraph at Royal Institution. Tapping didn’t sound right to his assistant’s assistant. A magician (Nevil Maskelyne) was tapping “rats” in morse code. Then changed to “There was a young fellow if Italy who diddled the public quite prettily.” Marconi claimed nobody could interfere – don’t promise what you can’t deliver! And an early white hat hacker to identify that.
  • 1939 – Bletchley Park – crack Enigma during World War II
  • 1957 – Joe Engressia learned if one whistles at a certain frequency, can get free long distance calls. In 60’s and 70’s if couldn’t whistle at 2600 hertz, produced blue box to hack this.
  • 1968 – Morris worm – one of first worms
  • 1992 – First polymorphic virus – constantly changes as infect each new machine so anti-virsu looking for standard signature can’t see it
  • 1994 – First kit for script kiddies. Didn’t need to be very skilled to attack.
  • 2002 – Bill Gates finally made security a top priority at Microsoft

Present

  • Don’t even have to go back 24 hours to find a data breach.
  • Mark Zuckerberg’s bad password
  • Credential stuffing – relatively new type of attack with multiple specialists. Has multiple parts.
    • Attackers usually have .1%-2% success rate in finding password reuse.  (using one stolen password on another site)
    • If steal a million stolen passwords, can quickly take over 10K accounts without anyone knowing.
    • Invisible – don’t know account is hacked.
    • Using botnet so target site can’t detect pattern of bad attempts either. Looks like a popular day on your website and not a hacking attempt
    • Over 500 million leaked passwords on dark net. So starting with known good passwords
    • Good – Netflix reset passwords based on ANOTHER company’s breach
    • Sentry MDA has credentials stuffing tool. Raw materials: credentials that are out there, IP addresses in proxy list and even help to get past captchas. Third party system for getting passed captchas as well mixing OCR (computers doing it) and mturk (humans doing it in developing countries)
    • Organic traffic has pattern/cycles throughout day. Inorganic traffic has different shape. Can see normal shape if look at graph without login URLs.
    • Botnets are distributed globally so can’t block IP by region.
    • Other things like monitoring also produces a spike.
    • Every website has a tiny bit of attacks. These crawlers are just the background radiation of the internet. This is an opportunistic probe. A bigger attacher has a profit motive so will stop or re-tool. The idea is to make is as expensive as possible for the attacker.

Future

  • Because the present isn’t scary enough, the future is scarier
  • Attack surface is related to complexity
  • “Every program attempts to expand until it can read mail. Those programs which cannot so expand are replaced by ones which can” – Jamie Zawinski.
  • Weak AI is already here. (ex: AIs representing users) Strong AI is much further out.
  • Sci fi: Black Mirror. Device records everything and you can replay it on demand. Privacy and security implications. Imagine if this data could be changed or published.
  • New attack surfaces:
    • autonomous vehicles
    • always on IoT devices like Amazon Echo could do surveillance
    • Apple Home – can unlock your home doors. Can turn on your lights/stereo at night randomly like horror movie. Someone could have a heard attack because think house is possessed
  • New technology creates new attacks
    • Audio/video fidelity – could steal fingerprints from far away or record every conversation from far away
    • Battery life – run surveillance device for weeks
    • CPU power – defeat encryption
  • New attacks create unforeseen consequences – now we have to take off shoes before flying

What can we do?

  • Pareto Principle – focus on where get most benefit
  • Cybercriminals innovate. So do security services/standards/platforms
qcon tuesday 2016 – live blog table of contents

I’m attending QCon New York 2016 for one day (Tuesday). I got a free pass for being selected for a BoF (Birds of A Feather) tonight. This post is the table of contents for all the sessions I attended (and will be filled in with blog posts as the day goes on)

Interesting logistics

  • InfoQ is 10 years old
  • Community night – 7:15-9:55 is open to non conference attendees
  • I’m doing one of four BoFs. Plus conference session on papers, JavaSig and vendor sessions. Lots of things at the same time. To incentivize people to stay, they are raffling a conference ticket.
  • Wireless has a 20 minute timeout. And there’s 25 minutes between session. Sounds like a lot of re-connecting over the day.

Note: I’m blogging from a computer rather than an iPad (since I needed the computer for the BoF) – so typing quality is better than usual.

sonar plugins and why i had to fork the sonar web plugin to add a rule

Last weekend, a few of the CodeRanch moderators were discussing a Trac item that we’d like to get rid of the I18N messages from our HTML. It’s there at all because open source JForum had it. We haven’t been updating it and have been using it inconsistently. Also, we do want to externalize the ones in Java which is why we can’t just get rid of the file wholesale – someone could add more references from HTML. I suggested that this would be a good thing to set up a SonarQube rule and volunteered to create the rule. This was a far harder and more interesting task than I expected it to be when I said I’d do it.
webProps

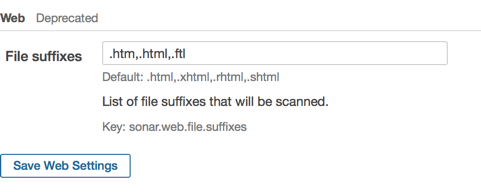
The web plugin scans HTML files and has a bunch of pre-defined rules and templates for them. You can set any file extensions you’d like so I had set “.html,.html,.ftl” in Administration > Configuration > Web to hit both our HTML and Freemarker code. Alternatively, you can set this in your Sonar properties file.

Looking through the rules and rule templates in the web plugin, there wasn’t one for what I wanted – plain String or regular expression search. Nuts! There are a few existing rules that do what I want, however I couldn’t use them:

Rule Why can’t use
Some Java packages or classes should not be used in JSP files In web plugin, but only for jsp/jsp files
Disallowed methods should not be allowed In Java plugin so only works for Java code
XPath rule Only works for XML files
The text plugin regular expression rule So close! This does exactly what I need. Except (see next section)

Great, the text plugin meets my needs. But alas. You can only associate a file extension with one plugin for each Sonar run. The HTML/Freemarker files are already considered web files.

So what’s wrong with the text plugin?

The text plugin has a rule called “Simple Regex Match”. When configured with the proper regular expression, it does exactly what I want. Except for one huge problem. In order to use it, I have to associate the text plugin with HTML/Freemarker files. This is a two step procedure:

  • In the browser, Administration > Configuration > Web – set the web extensions to “foo”. Leaving it blank is insufficient as it defaults to include HTML and Sonar does not let the same file extension be associated with multiple plugins.
  • In sonar-project.properties, add the line: sonar-text-plugin.file.suffixes=.htm,.html,.ftl

You also have to run sonar-runner twice. Once with the HTML/Freemarker files associated with the web plugin to get those results and again with them associate with the text plugin to get the rule I’m trying to write. This means you need to have the code show up as two projects within SonarQube. (otherwise Sonar will tell you the rule violations were fixed for whichever analysis you run last.)

Extending the web plugin

Ok. I clearly need to extend the web plugin so that I can have a regular expression rule associated with the web plugin. The docs say the web plugin doesn’t support extending it with Java or XPath rules as does this post. I tried anyway hoping this was out of date. I was able to get my new rule to show up in Sonar, but not to run. Everything I’d need to do in order to get it to run was considered a duplicate and prevented Sonar from even starting up. For example, “org.sonar.api.utils.SonarException: Can not add the same measure twice” or “duplicate keys not allowed”. So I concede this path is a non-starter. It would have been nice to have my custom rule in a separate Maven project rather than having to fork the existing one.

Forking the web plugin

Sigh. Last resort. Time to fork. This newsgroup post pointed to a commit that shows how to add a rule to the web plugin. I wanted to add a rule template rather than a rule, but the idea is the same. It wasn’t hard to make the change within the project. It’s just that forking isn’t good in the long run as I’ll have to keep re-merging. What I needed to change in my fork:

  1. Add custom rule template class to org.sonar.plugins.web.checks.coding package. The code was pretty similar to the rule for illegal spaces:
    package org.sonar.plugins.web.checks.coding;
    
    import java.io.IOException;
    import java.nio.charset.Charset;
    import java.util.List;
    
    import org.sonar.api.utils.SonarException;
    import org.sonar.check.Priority;
    import org.sonar.check.Rule;
    import org.sonar.check.RuleProperty;
    import org.sonar.plugins.web.checks.AbstractPageCheck;
    import org.sonar.plugins.web.checks.RuleTags;
    import org.sonar.plugins.web.node.Node;
    import org.sonar.plugins.web.visitor.CharsetAwareVisitor;
    import org.sonar.squidbridge.annotations.NoSqale;
    import org.sonar.squidbridge.annotations.RuleTemplate;
    
    import com.google.common.io.Files;
    
    @Rule(
      key = "RegularExpressionNotAllowedOnLineCheck", 
      name = "Regular expression \"regex\" not allowed on web page", 
      priority = Priority.MAJOR, tags = {
      RuleTags.CONVENTION })
    @RuleTemplate
    @NoSqale
    public final class RegularExpressionNotAllowedOnLineCheck extends AbstractPageCheck implements CharsetAwareVisitor {
    
    	@RuleProperty(
          key = "regex", 
          description = "Single line regular expression to prohibit on web pages")
    	public String regex = "";
    	
    	private Charset charset;
    
    	@Override
    	public void setCharset(Charset charset) {
    	   this.charset = charset;
    	}
    
    	@Override
    	public void startDocument(List<Node> nodes) {
    		List<String> lines;
    		try {
    			lines = Files.readLines(getWebSourceCode().inputFile().file(), charset);
    		} catch (IOException e) {
    			throw new SonarException(e);
    		}
    		for (int i = 0; i < lines.size(); i++) {
    			// only support matching text within a single line to facilitate identifying line number
    			if (lines.get(i).matches("^.*" + regex + ".*$")) {
    				createViolation(i + 1, "Replace all instances of regular expression: " + regex);
    			}
    		}
    	}
    
    }
    
  2. Add the rule template to org.sonar.plugins.web.rules.CheckClasses so the web plugin knows about.
  3. Create a new HTML file in the resources localization directory.
  4. Write/update tests. I like that the sonar-web-plugin project uses JUnit tests to enforce some of there conventions like rules ending in “Check”.

Where is the code?

I’ve placed my fork on Github. It’s 2.5-SNAPSHOT because I didn’t see any need to version it. I also created a pull request for the sonar-web-plugin in hopes they are interested in merging it. The plugin was last released a year ago so I imagine I’ll be using my fork for along the foreseeable future in any case. Which is fine. CodeRanch is a volunteer run website so no rules against using forked software.